Harper Griffin · 24 October 2026
Exploring Encryption Standards and User Privacy Controls in Evolving Note Organization Platforms
Digital note organization platforms continue to integrate advanced encryption methods while users demand clearer privacy controls over their stored information. These systems handle everything from personal journals to corporate project details, and the standards they adopt directly affect how data remains protected during storage and transmission.
Current Encryption Standards in Note Platforms
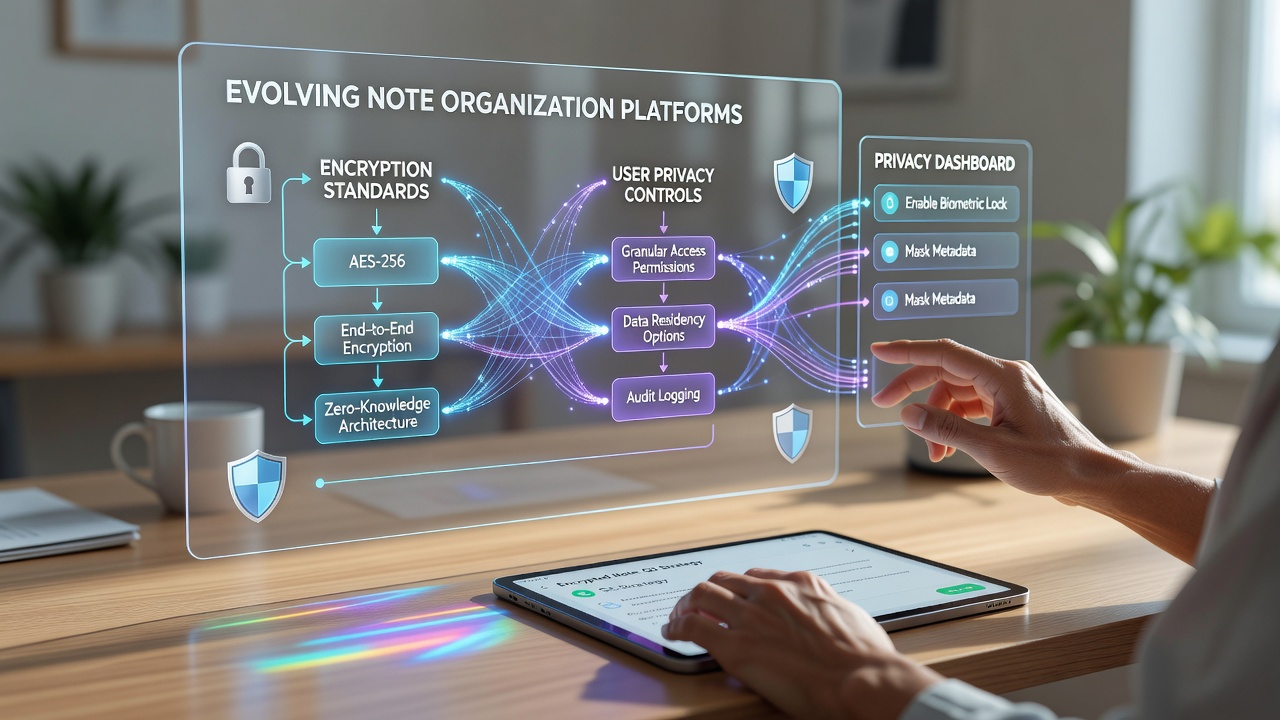
Many platforms rely on AES-256 encryption for data at rest, a specification developed through NIST processes that researchers continue to validate for resistance against known attack vectors. End-to-end encryption appears in select tools where private keys stay on user devices, preventing server access to plaintext content even during routine maintenance cycles.
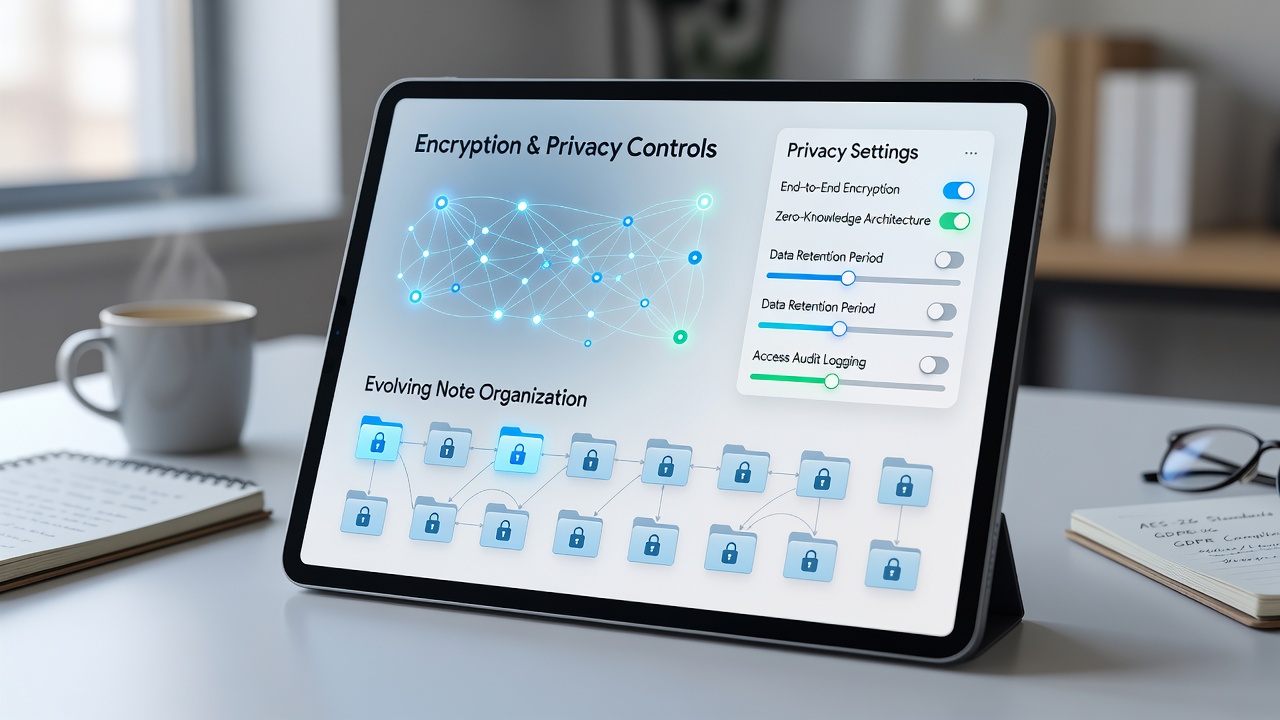
Transport Layer Security protocols secure data in transit across most services, and developers often combine these with additional measures such as zero-knowledge architectures that limit provider visibility into user content. Observers note that adoption rates for these combined approaches have risen steadily since 2023 as regulatory requirements tightened in multiple jurisdictions.
Privacy Controls and User Management Features
Platforms now offer granular permission settings that let users restrict access at the note level or apply role-based controls across teams. Two-factor authentication has become standard, while some services introduced biometric options tied to device hardware for account recovery processes.
Data residency choices allow organizations to select storage regions that align with local compliance needs, and audit logs track who accessed which notes along with timestamps for each action. These features emerged in response to frameworks like the EU's GDPR and similar rules from Canada's PIPEDA, which require explicit consent mechanisms for data handling.
Platform Comparisons and Implementation Differences
One study from a university research group examined how different note tools balance encryption strength against usability, finding that systems with client-side key management tend to require more user training yet deliver stronger isolation of sensitive material. Another report from an Australian research institution highlighted variations in how platforms handle metadata encryption, noting that some leave file names and timestamps exposed even when note content stays protected.
Developers face ongoing choices between open-source encryption libraries and proprietary implementations, and those decisions influence how quickly vulnerabilities receive patches across the ecosystem. Platforms that publish their cryptographic implementations for external review often see faster identification of potential weaknesses before widespread deployment.
Regulatory Developments and October 2026 Updates
Upcoming changes scheduled for October 2026 include revised guidelines from several standards bodies that may require platforms to support quantum-resistant algorithms alongside existing methods. These updates stem from work at NIST on post-quantum cryptography, and note organization services have begun preliminary testing of hybrid encryption schemes that combine classical and newer approaches.
Users in regions following updated data protection rules will gain expanded rights to request encryption key deletion or transfer of protected data to other services. Industry groups have started publishing compliance checklists that platforms can adopt to demonstrate alignment with these evolving expectations.
Challenges in Maintaining Both Security and Accessibility
Balancing strong encryption with seamless cross-device synchronization requires careful key distribution methods, and services that fail to implement these correctly sometimes experience lockouts during device transitions. Researchers have documented cases where weak default settings left certain user groups more exposed despite advanced backend protections.
Third-party integrations add another layer of complexity, since note platforms must verify that connected apps respect the same privacy boundaries without introducing additional data exposure points. Organizations tracking these integrations often review API documentation and conduct periodic security assessments to confirm ongoing compliance.
Conclusion
Encryption standards and privacy controls in note organization platforms continue to advance through a combination of technical improvements and regulatory pressures. Data from multiple sources shows consistent growth in the adoption of stronger methods, while users gain more tools to manage access and residency preferences. As platforms prepare for the October 2026 milestones, the focus remains on delivering verifiable protections that scale across diverse user needs without compromising core functionality.